
Below is the description of the steps to Configure SSO in Mavvrik:
-
Login to Mavvrik as an owner
-
Click on Menu > Admin > SSO
-
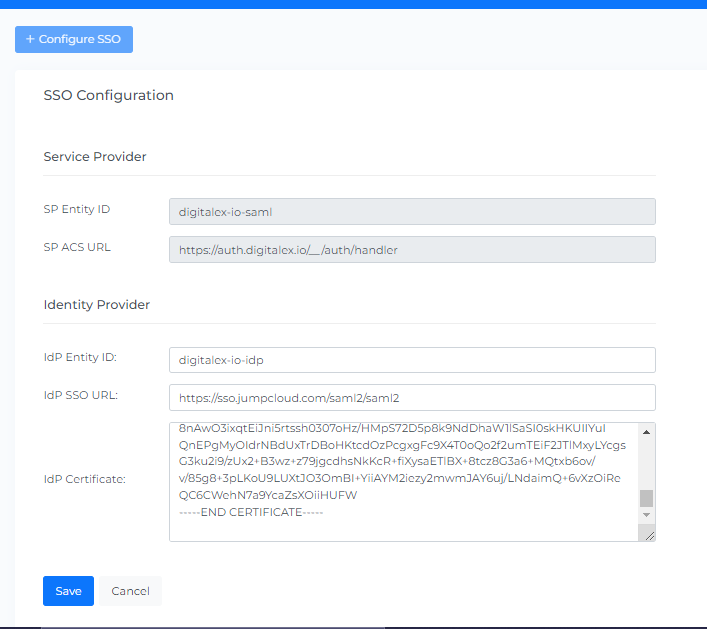
Click on Configure SSO button
-
Enter IdP Entity ID copied in Step-4
-
Enter IdP SSO URL copied in Step-4
-
Enter IdP Certificate downloaded in Step-4
-
Click Save
-
SSO is Configured Successfully, You can Edit or Delete the existing data if required
-
Click on Login with SSO
-
Pop-up/new page appears which navigates to Jump Cloud Sign in page to let you sign in using your Jump Cloud account
-
Enter your Jump Cloud credentials and click login
Note:
-
Users who are added in Mavvrik are able to login successfully with their Jumpcloud accounts and access the Application based on their privileges
Edit SSO Configuration
Enable Enforce SSO
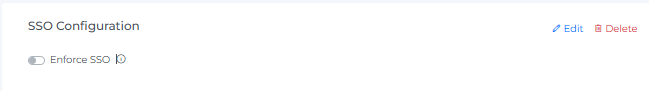
Once enforced, users will be required to authenticate exclusively through SSO, and no other login methods will be allowed.
Enable User Provisioning
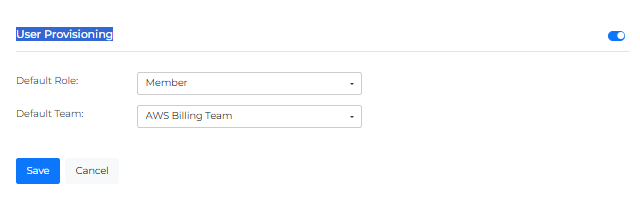
When User Provisioning is enabled, new users logging in via SSO will be automatically created in the Mavvrik platform during their first successful login attempt.
Previously, users had to be explicitly created in both the Identity Provider (IdP) and the Mavvrik platform before they could log in using SSO. This enhancement removes that requirement and reduces onboarding friction.
Password-based login is available only when Enforce SSO is disabled. In that case, users can set their password using the “Forgot Password” option after their account has been automatically created.
When this option is disabled, new users signing in through SSO will not be automatically provisioned in Mavvrik.
Troubleshooting
SSO login through JumpCloud fails
-
Start with Login with SSO on the Mavvrik login page and use the intended JumpCloud account.
-
Compare the IdP Entity ID, IdP SSO URL, and certificate saved in Mavvrik with the identity-provider details collected for the same JumpCloud application.
-
In JumpCloud, verify that the service-provider Entity ID and ACS URL match the values copied from Mavvrik.
-
Confirm that the intended user's group is selected for the SAML application and that the Activate and Continue steps were completed. Save any corrected configuration and retry from Mavvrik.